The Attack Surface is comprised of all IT-systems, components and services that may be used or abused by an attacker to perform cyber attacks. This primarily includes all IT products and infrastructure, regardless of their general immediate vulnerabilities, but also vulnerabilities like those coming from organization or human failure. The biggest Attack Surfaces attackers can find are Domains and URLs (cf. Attacks on Web Attack Surfaces) as well as email adresses, accounts in social media and messengers (cf. Digital Communication). For years, connected devices like smart-home devices or connected devices in healthcare and telematics infrastructures provide attack surfaces towards cyber attacks that utilize vulnerabilities in ip-based communications (cf. Connected Devices). The growth of vulnerable attack surfaces during the current reporting period was attributed especially to the sharp rise of newly discovered vulnerabilities (cf. New Vulnerabilities), more especially newly discovered hardware vulnerabilities (cf. Hardware Vulnerabilities). AI agents found numerous new vulnerabilities within shortest amounts of time (cf. Attack Infrastructures).
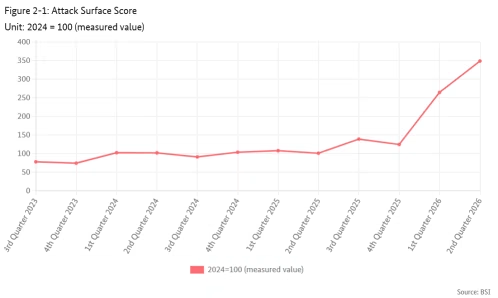
The Attack Surface Score is a normalized key figure on various attack surfaces in Germany. In addition to general digitalization, it takes vulnerabilities, their severities, and damage potentials in particular into account.
…
[more]
Attack Surface Score
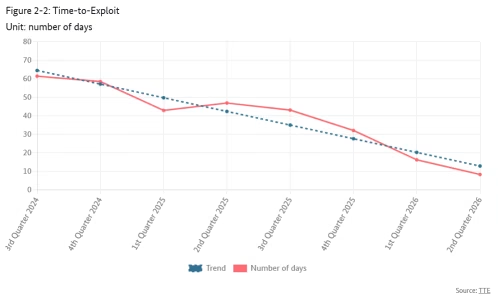
Time-to-exploit (TTE) measures how much time attackers need after the publication of a vulnerability to develop and deploy functional malicious code (exploit).
…
[more]
Time-to-Exploit
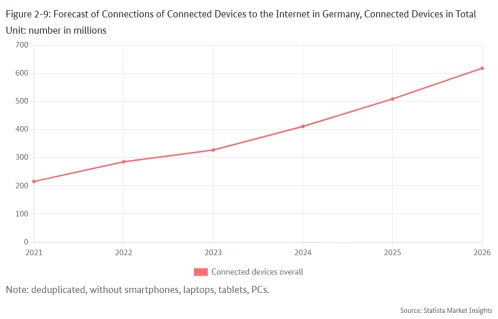
Connected devices offer an attack surface that has been growing for years. According to forecasts, there will be a total of just under 618 million connections
…
[more]
Connected Devices
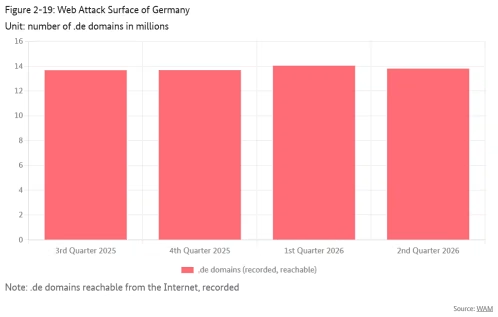
The web attack surface attributable to Germany includes all .de domains. It included an average of 17.7 million domains in the current reporting period.
…
[more]
Web Attack Surfaces
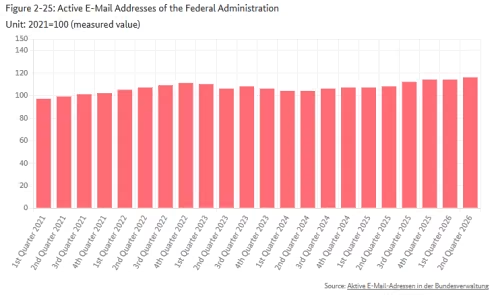
E-mail addresses are an attack surface for, among other things, phishing and malware attacks. They are accordingly one of the main targets for cyberattacks.
…
[more]
Mail Attack Surfaces of the Federal Administration