

Under §7 BSIG, the BSI subjects the information security management systems (ISMS) of particularly prioritized federal authorities to an examination. The process of this standard revision (cf. Figure 5-32) initially includes a comprehensive interview with the corresponding information security officer (ISB) and the respective subject matter specialists of the authority. Subsequently, all relevant documents (guidelines, process descriptions, service instructions, etc.) are examined and checked. While documents reflect the theory, interviews often show the lived practice. Finally, an effectiveness check is carried out to assess the implementation of the information security processes.
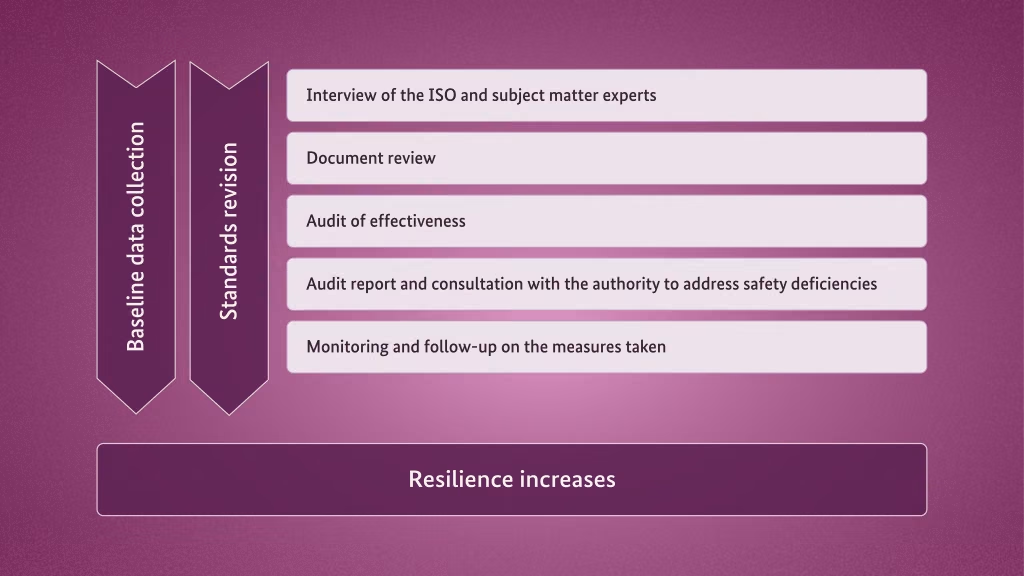
Figure 5-32: Increased resilience through standards revision, baseline data collection, consulting for implementation as well as auditing, monitoring and accompaniment of measures.
The identified security deficiencies and potential recommendations culminate in a comprehensive audit report. This is the basis for a further targeted implementation consulting of the authority by the BSI in order to durably eliminate security deficiencies. Subsequently, a measures implementation plan (MUP) is created together with the audited authority. This contains the deficiencies identified in the report, a prioritization, and measures for the solution. With the help of the MUP, a regular follow-up process is established in order to support the authorities as best as possible in a solution-oriented manner from the side of the BSI.
The review of the security measures of the authorities and a subsequent elimination of security deficiencies thus contributes significantly to a resilient Federal Administration.